Standing Credentials Are the Last Blast Radius
An AI agent doesn't need malicious intent to cause damage. A single over-scoped credential can turn a routine task into a production incident. GovernXperts limits that blast radius.
See How GovernXperts Evaluates Request
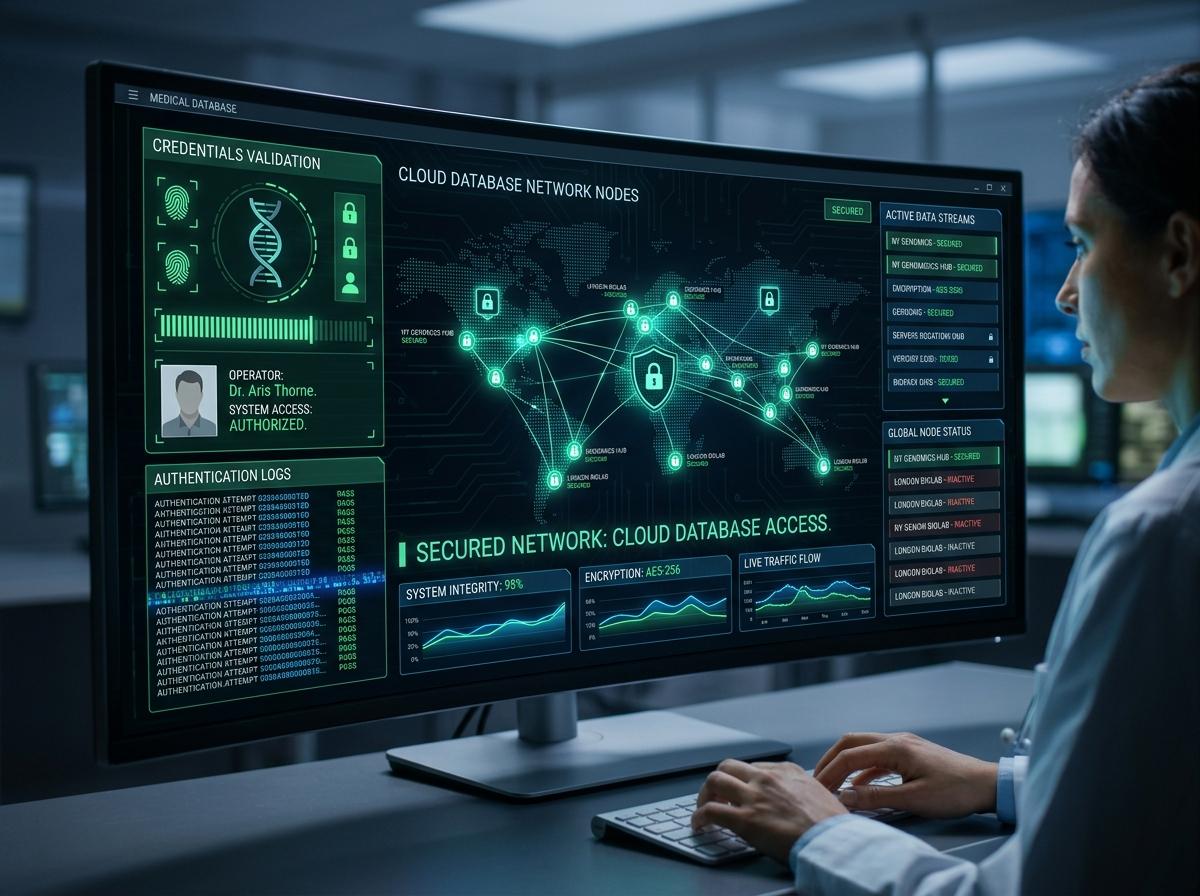
Simulate an autonomous healthcare assistant attempting to fulfill a prompt. Toggle between standard standing service tokens and GovernXperts policy checks.
Request matches the assigned patient appointment scheduling task. Scope 'records:schedule:read' granted on a zero-standing-privilege token.
When autonomous healthcare assistants run on persistent database credentials, any prompt deviation exposes patient records across silos.
GovernXperts verifies the agent's assigned task against requested API endpoints before issuing ephemeral single-use tokens.
Every granted and blocked request is cryptographically recorded with prompt context, actor identity, and payload checksums.
Deterministic Safeguards Built for High-Stakes Operations
Zero Standing Service Tokens
Eliminate long-lived API keys in production agent scripts. Tokens are minted just-in-time per API call and invalidated milliseconds after response reception.
Task-Bounded Scope Verification
Even if an LLM is jailbroken or injected, GovernXperts intercepts the call at the edge and enforces policy boundaries before the network packet reaches hospital EHRs.
Tamper-Proof Audit Trail
Produces immutable cryptographic logs with millisecond timestamps, model ID, prompt hash, and policy evaluation verdicts ready for HIPAA and SOC2 audits.
Proven Security Outcomes
- ✔Reduced the operational blast radius of AI mistakes
- ✔Eliminated implicit trust in persistent credentials
- ✔Strengthened governance for autonomous agents
- ✔Improved compliance through complete auditability
- ✔Increased confidence in deploying AI into production
Key Architectural Takeaway
“Agent intelligence should never imply operational authority. Every privileged action should be independently authorized, validated, logged, and recoverable.”
Frequently Asked Architecture Questions
Learn how deterministic policy enforcement integrates into healthcare workflows without requiring changes to foundational model providers.
GovernXperts acts as a reverse proxy or sidecar policy evaluation engine. Outgoing HTTP/gRPC requests initiated by your AI agents route through the GovernXperts runtime, where policy engines inspect the request path and context before delegating to the target backend.
Explore More Sector Blueprints
Finance: High-Value Wire Transfers
Analyze Blueprint EducationEducation: Transcript DB Mutations
Analyze BlueprintTest Live Policy Rules
Experiment with live agent actions inside our interactive security console.
Implement Deterministic Controls in Your Organization
Every action an AI agent takes should be validated, traceable, and reversible. Talk to our systems architects about deploying GovernXperts in your environment.
Book a Custom Demo ➔